HackZero.ai is now Compliance Everywhere. Read why →

SOC 2 for startups

SOC 2 for startups.
Your agent builds it. A US CPA signs it.

Connect your AI agent once. It builds the controls, drafts the policies and collects the evidence. We pentest your app every month and check your laptops. An independent US CPA signs the Type I or Type II report your buyers keep asking for.

$299/mo, plus the independent CPA audit. See pricing ›

ISO 27001, HIPAA and GDPR will be included at no extra cost when they launch.

Switching from Drata made so much sense.
Elyas Shaiwani, CEO, Curago Health
saves a sh*t ton of time ;)
Diego Gomes, Partner, SaaSholic

One tool, not four

Everything your SOC 2 needs. One subscription.

The usual stack is a GRC platform, a pentest firm, a device manager and an auditor, four invoices and four logins. Here it is one strand: your agent, our team, an independent CPA, and a public Trust Center at the end of it.

Controls

You connect GitHub, AWS and Google Workspace. Your agent does the rest over MCP: builds the controls, drafts the policies and uploads the evidence.

$299 / mo. The GRC for SOC 2.Trust Center included. ISO 27001, HIPAA and GDPR at no extra cost when they launch. GRC platform, about $10,000 a year
Pentest

We attack your production app every month, in house, and the fixes land as pull requests.

Free. One AI pentest a month.A human pentest is $1,500 per engagement. Pentest firm, $15,000 to $30,000 a year
Devices

We manage the laptops. Disk encryption, screen lock and updates, enforced and checked.

Free. Included for every laptop. Device manager, about $4,000 a year
Independent CPA

A licensed, AICPA‑member US firm signs the report. Not us, not a partner we pay. They bill you directly.

From $700 for Type I, $2,100 for Type II, once.Billed by the independent CPA, not us. Check pricing calculator ›
Trust Center

The signed report goes live on a public page your customers can check, with your controls and policies beside it.

Free. Included. Trust page vendor, about $3,000 a year
Replaces $32,000 to $47,000 a year of vendors. Under 10 people, a first-year Type II is about $7,188 all in. See what yours costs›

Your agent, over MCP

Do it all from your agent, over MCP.

SOC 2 readiness in under 10 hours. Your agent does most of it.

Connect it once and tell it to get you SOC 2 ready. Every piece of evidence it files carries the exact command, so your auditor can run it again.

Works with ClaudeCursorGeminiCodexand any MCP clientSee the MCP server›

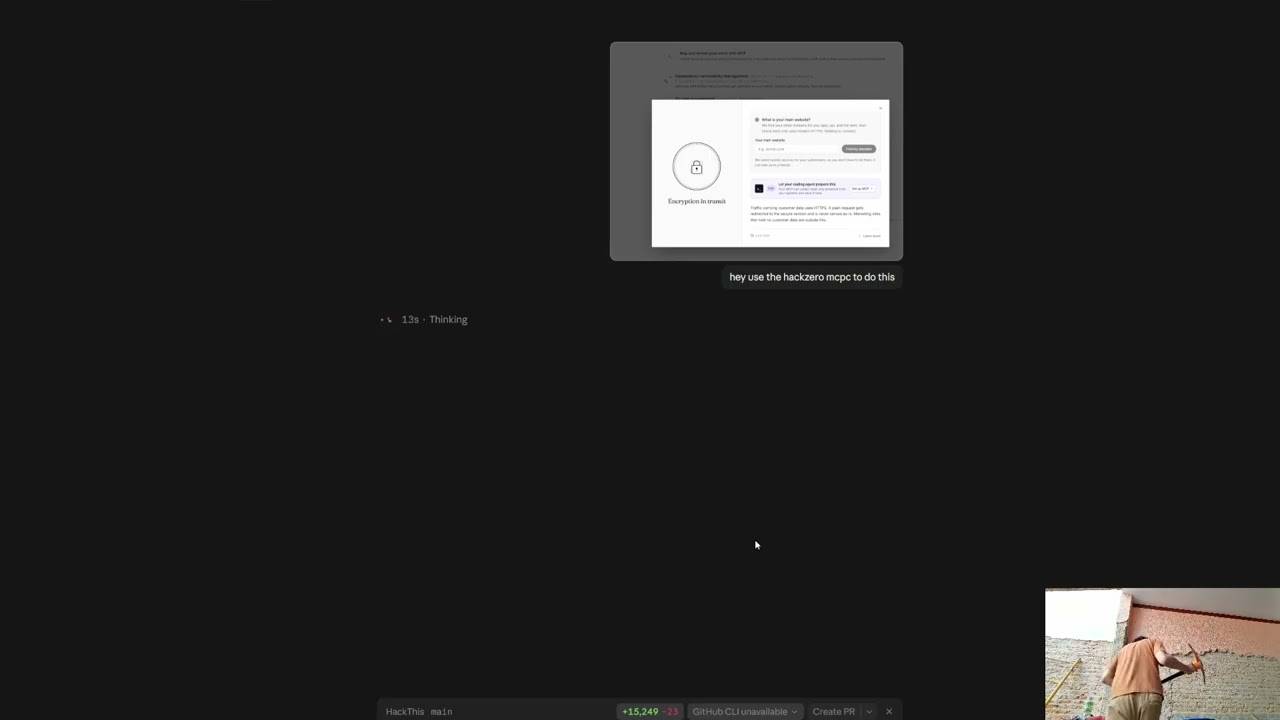
A Claude Code terminal driving Compliance Everywhere over MCP. The user asks the agent to get them SOC 2 ready. The agent checks where they stand, runs a read-only command and files its output as evidence with the command attached, and drafts a policy for them to sign.

What your agent does.

  • Builds the controls and drafts the policies.
  • Runs read-only commands with the logins you already have, and files the output with the exact command attached.
  • Proposes your systems, vendors and people for you to confirm.
  • Asks the setup questions only you can answer, and waits for your answer.
What stays with you.

  • Answer the setup questions, a few at a time, as multiple choice.
  • Sign the policies, in the browser. No key can sign for you.
  • Do what has to actually happen: the access review, the incident response exercise, security training, the management review and the backup restore test.

Type I or Type II

Two reports. What each one proves.

Same controls, same platform, same CPA. The difference is the time the report covers. The long version is in SOC 2 compliance, explained.

Type I. Designed right, on one day.

The CPA checks that your controls are designed correctly at a single point in time. There is no window to wait out, so it is the fast way to unblock a deal.

What it proves
Your controls are designed right, on the report date.
How long
Roughly 4 to 8 weeks.
When to pick it
A deal is waiting now. Commit to the Type II next.
The CPA's fee
From $700, once, billed by the CPA.

Type II. Proven to work, over time.

The CPA checks that your controls actually worked across a stated period, the observation window. Most customers ask for this one, and most companies renew it every year.

What it proves
Your controls operated through the whole window.
How long
The window runs 3 to 12 months. A first Type II with a 3-month window lands about 4 to 6 months from a standing start.
When to pick it
Your buyer asks for Type II, which most do.
The CPA's fee
From $2,100, once, billed by the CPA.

The path to a report

From sign-up to a signed report.

All the state lives on our server, so the work can stop and start across sessions and laptops without losing a step. Every cost along the way is in what a SOC 2 costs.

  1. 01Connect

    Sign up, connect GitHub, AWS and Google Workspace, and connect your agent to the MCP server.

  2. 02Build the controls

    Your agent works through the controls with you. Policies get drafted, answered and signed.

  3. 03Close the gaps

    The first AI pentest runs against your app, the Device Checker covers every laptop, and the red controls turn green.

  4. 04The audit

    The independent CPA tests your controls: on one day for Type I, across the observation window for Type II.

  5. 05The signed report

    The CPA signs the report, and it goes live on your Trust Center.

Watch the demo

The whole setup, in 2:19.

Four questions, one guided path through the controls, and Claude doing the work over MCP. Chapters and the full transcript are on the demo page.

Frequently asked

Questions.

01Type I or Type II?

Type I says your controls are designed right, on one day. Type II says they actually worked over a period, usually three to twelve months. Most customers ask for Type II. Many teams get a Type I first to unblock a deal, then the Type II.

02Which trust criteria do I need?

Security is in every SOC 2. Add Confidentiality if you hold customer data under contract or NDA, and Availability if customers ask about uptime commitments. Most startups start with Security alone.

03Who signs the report?

An independent US CPA firm that is an AICPA member. They contract with you and bill you directly, and we never take a share of that fee, because a fee split would compromise the independence that makes the report worth anything.

04Will my customer accept this report?

It is a SOC 2 report with an opinion from an independent, AICPA-member US CPA, the same thing they ask every vendor for. We give you the documentation and evidence they may want and join the call if it helps.

05Why so cheap? Is this a SOC 2 report mill?

No. It is a high-quality, minimal-scope SOC 2. It is not enterprise-grade coverage for 100 employees and 100 microservices, and we do not pretend it is.

06Do I need a separate pentest?

You don't need a separate vendor. Auditors will expect a human pentest for both Type I and Type II, and we run it in house for $1,500, mapped to your SOC 2 controls. On top of that, an AI pentest of your app runs free every month.

07How long does it take?

A Type I takes roughly 4 to 8 weeks. A Type II cannot be shorter than its observation window, which runs 3 to 12 months, so a first Type II with a 3-month window realistically lands 4 to 6 months from the day you start.

Tell us your deadline.
We'll tell you what it takes.

Thirty minutes with the founders on your scope, Type I or Type II, and what the independent CPA's report costs.