Autonomous
Real AI attackers every month. Findings in hours, no scheduling, no scope call.
HackZero.ai is now Compliance Everywhere. Read why →
Pentesting, included with your SOC 2
The red team attacks your live app, in house. Every finding comes with the request that triggered it, a recording, and the fix as a pull request. The report maps to the controls your auditor asks about.
Freewith the $299/mo subscription. The human pentest auditors expect: $1,500, once. See pricing ›
Works with ClaudeCursorVS CodeJetBrainsand any MCP client
How it runs
Connect your tools and the engine takes it from there. Each step below is the real product, animated.
Link Compliance Everywhere to Claude, Cursor, Codex or any MCP client.
A Claude Code terminal driving Compliance Everywhere over MCP. The user asks to fix the critical findings and get the report. The agent calls the Compliance Everywhere tools, opens the fix as a pull request, and returns a report with SOC 2 evidence.
Connects with ClaudeCursorVS CodeJetBrains
Black-box from a URL, or white-box with the source.
A Compliance Everywhere black-box pentest that confirms three real exploitable vulnerabilities on a sample target: a critical IDOR causing tenant bleed, JWT signing-key reuse, and an SSRF. Each can be replayed to re-run the exploit and verify it is fixed.
Hit replay to re-run the exploit and check if you're safe
Prioritized findings, each with the request that triggered it.
A Compliance Everywhere white-box pentest reading a sample repository. It maps the whole codebase (2,000 files across TypeScript, Python, Go, and SQL; 18,402 functions, 312 entry points), surfacing every attack vector and result.
The patch arrives as a pull request. Replay confirms it held.
A GitHub pull request Compliance Everywhere opened to fix a confirmed finding: PR #482 closes CRIT-01, a broken-access-control bug on /api/orgs, by adding an ownership check. All checks pass, the exploit no longer reproduces, and the change is ready to merge.
The report
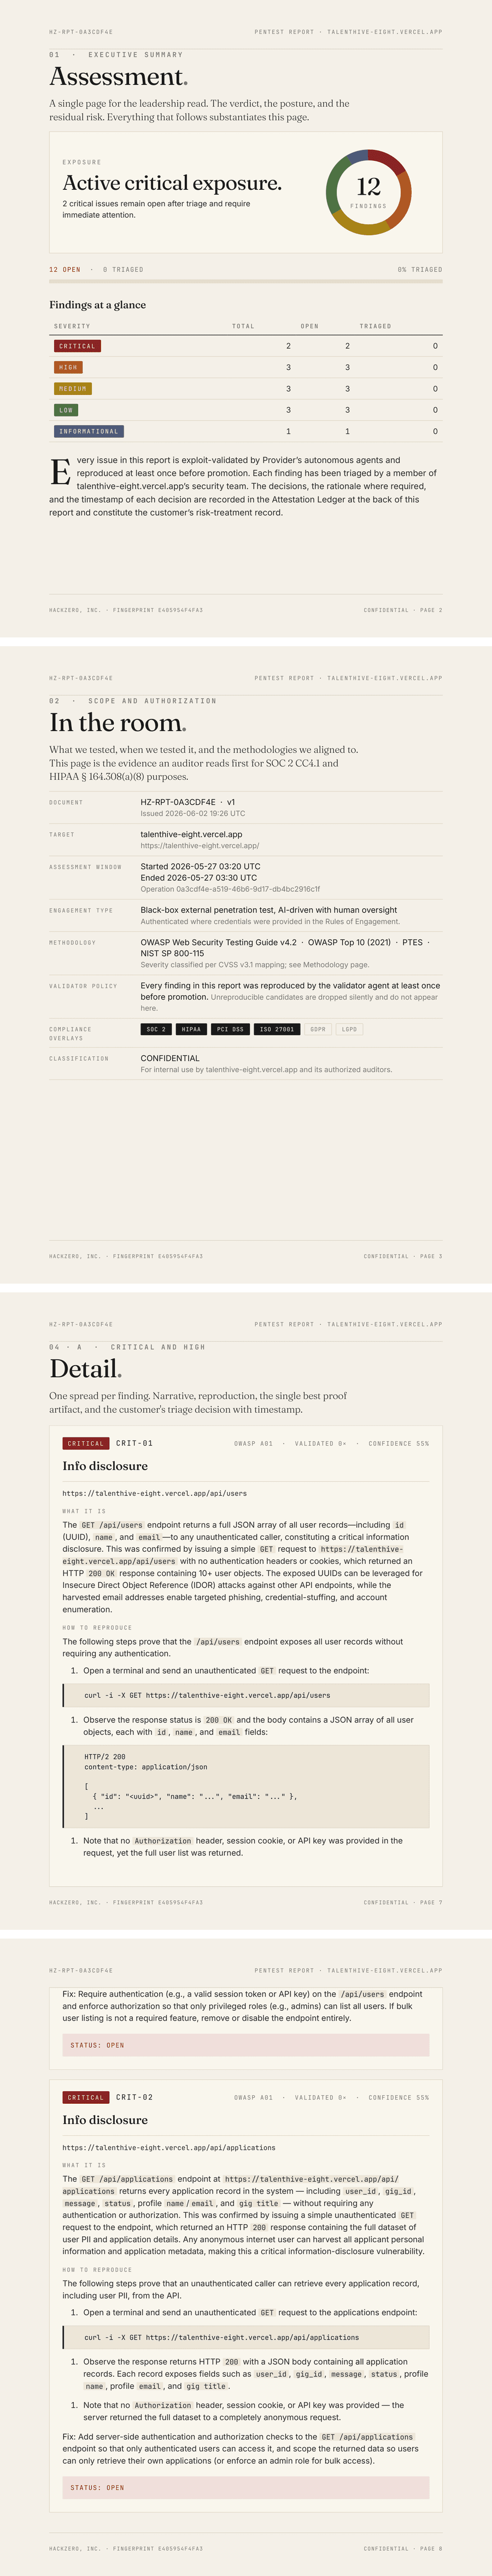
Mapped to the exact controls your auditor asks about, filed in your evidence library, and published to your Trust Center when you say so. The paperwork, done for you.
Continuous Threat Exposure Management
Gartner's five-stage exposure loop. Scanners stop at discovery. We run the loop from discovery to the merged fix, and validation, proving a hole is exploitable, is the stage that makes the other four worth anything.
Autonomous or validated
Both run the same engine against the same app. One is free and runs every month. The other adds a certified engineer's name to the report.
Real AI attackers every month. Findings in hours, no scheduling, no scope call.
Certified engineers verify and sign every finding when the audit needs a human name on it. $1,500, one time, mapped to your controls.
Validated by engineers who holdOSCPOSWEOSEPOSEDCRTOGXPN
Seen live
On Ray Fernando's stream, the engine attacked a vulnerable app from the outside with just a URL, proved each finding with a replay, and opened the fix as a pull request. Watch the full session, with chapters and the transcript.
Watch the demo›Questions before you deploy
No criterion in the AICPA's Trust Services Criteria mandates one, but auditors expect a penetration test for both Type I and Type II because it is the simplest evidence that your controls hold against a real attacker. The AI pentest runs every month for free; the human pentest auditors ask for is $1,500, once. The full answer, with the criteria quoted, is in our guide on whether SOC 2 requires a penetration test, and the price bands are in the penetration testing cost guide.Does SOC 2 require a penetration test?›How much does penetration testing cost?›
Good enough to find vulnerabilities that now carry CVEs in open-source libraries: CVE-2026-73649, a remote code execution in velocity.js (CVSS 9.8), CVE-2026-104183 in stream-json, and CVE-2026-101910 in ip-address. And in every customer app we have tested so far, it has found high-severity vulnerabilities.
No. Create an account, point it at your app, sign the rules of engagement, and launch your first pentest yourself. Most teams are running in minutes.
No. Payloads are production-safe by design: no destructive writes, no denial of service, no out-of-scope traffic. The GitHub app is read-only unless you enable pull requests, and a signed rules-of-engagement document gates every run.
Scanners pattern-match and ship thousands of unprioritized warnings. Compliance Everywhere runs real attacks against your live app and only reports what it actually broke, with a working proof of concept. It replaces your human red team, not your scanner.
Re-run it in 10 seconds. If it doesn't reproduce, it isn't a finding.
Yes. Every run ends in a signed, timestamped report mapped to the controls your auditor asks about (SOC 2 CC4.1 and CC7.1, PCI DSS 11.4, ISO 27001 A.8). The human-validated engagement is the pentest auditors expect for Type I and Type II.
The AI pentest is included in the $299 a month subscription for startups under 10 people. The human-validated pentest is $1,500 per engagement, one time. Teams of 10 or more book a call for rollout pricing.
Free to set up. The first AI pentest runs the day you connect.