 Claude
 Cursor
 Gemini
What your agent will do.
- Work through the controls and draft the policies.
- Run read-only commands with the logins you already have, and file the output with the exact command attached.
- Propose your systems, vendors and risks for you to confirm.
HackZero.ai is now Compliance Everywhere. Read why →
ISO 27001 for startups. Available Nov 9.
From November 9, the agent that runs your SOC 2 will work on ISO 27001 too, over the same MCP connection. Leave your email and we will tell you the day it opens.
$299/mo, the same subscription as SOC 2. See pricing ›
No extra cost for ISO 27001 when it launches. The certification body bills its audit directly.
One email when ISO 27001 opens. Nothing else.
That didn't go through. Check the email, or write to us at [email protected].
You're on the list. We'll email you when ISO 27001 opens on November 9.
What our SOC 2 customers say
Switching from Drata made so much sense.
saves a sh*t ton of time ;)
One subscription, from November 9
A compliance platform, a pentest firm, a device manager and a trust page, replaced by one strand. The only fee that leaves it is the audit, because that one has to stay independent.
From launch, your agent will work through the ISO 27001 controls and policies with you over MCP, the way it does SOC 2 today.
$299 / mo. The same subscription.No extra cost for ISO 27001.We attack your production app every month, in house, and the fixes land as pull requests.
Free. One AI pentest a month.A human pentest is $1,500 per engagement.Disk encryption and screen lock, checked on every laptop.
Free. Included for every laptop.An accredited certification body audits you and issues the certificate. Not us, and we take no share of its fee.
Quoted by the certification body.Billed by them, directly to you. Talk it through on a call ›The public page your buyers check, live today for SOC 2. The ISO 27001 certificate is planned to sit beside it.
Free. Included.Your agent, over MCP
SOC 2 readiness takes under 10 hours today. ISO 27001 joins on November 9.
Connect your agent once, for SOC 2 today. Every piece of evidence it files carries the exact command, so an auditor can run it again.
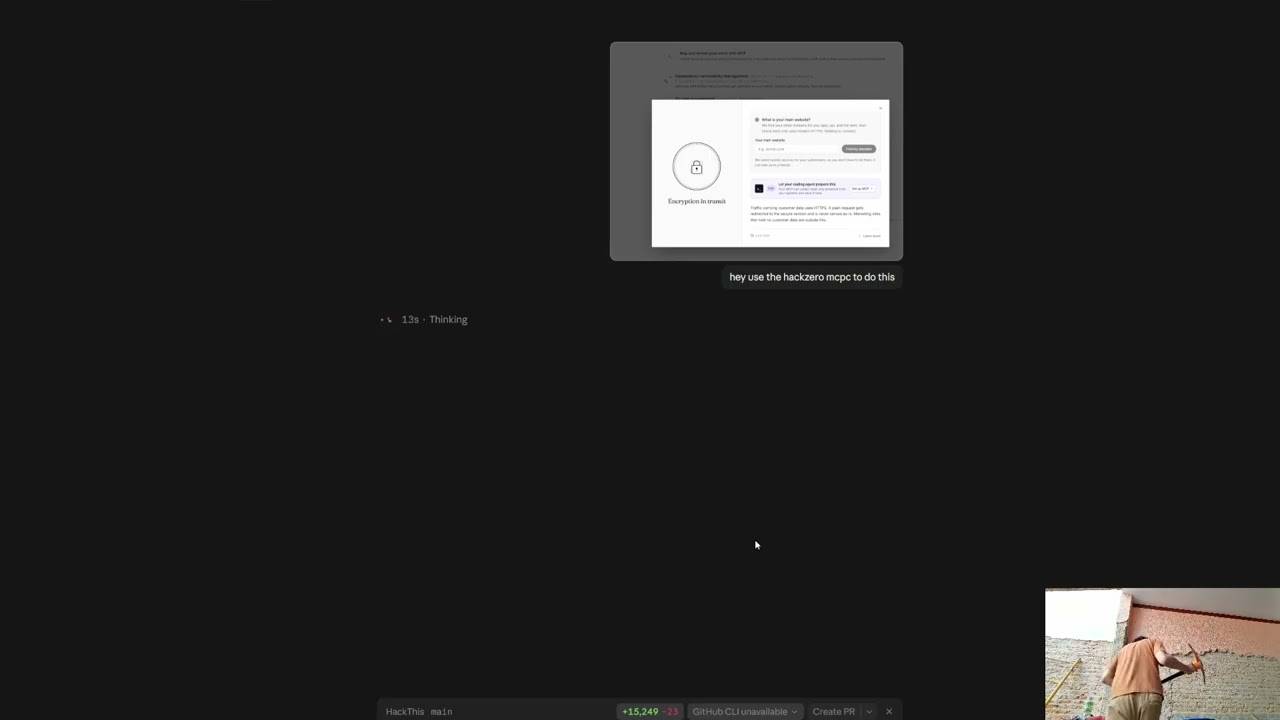
Works with ClaudeCursorGeminiCodexand any MCP clientSee the MCP server›A Claude Code terminal driving Compliance Everywhere over MCP. The user asks the agent to start their SOC 2 now, with ISO 27001 next. The agent checks where the SOC 2 stands, proposes risks and vendors for the user to review, and drafts a policy to sign. ISO 27001 joins the same connection on November 9.
SOC 2 or ISO 27001
ISO/IEC 27001 is the international standard for an information security management system. Both answer the same buyer question, in two different forms.
A CPA firm tests your controls and writes its opinion in an attestation report. There is no certificate.
An accredited certification body audits your information security management system and issues a certificate.
The path to a certificate
The certification audit runs in two stages, both done by the certification body. More on testing in does ISO 27001 require penetration testing?
Join the waitlist. If a buyer needs a report now, start SOC 2 today on the same agent.
Your agent will work through the controls with you. Policies get drafted, answered and signed.
The monthly pentest and the Device Checker cover the technical side.
The certification body reviews your documents and checks you are ready.
Stage 2 tests the controls in practice. Pass it and the certification body issues your certificate.
Watch the SOC 2 demo
This is SOC 2, live today, with Claude doing the work over MCP. ISO 27001 will run on the same agent. Chapters and the transcript are on the demo page.
Frequently asked
November 9. Join the waitlist on this page and we will email you when it opens. If you have a deadline before then, book a call and we will tell you where it stands.
No extra platform fee. ISO 27001 will be included in the same $299 a month subscription that covers SOC 2, for startups under 10 people. Teams of 10 or more get a price on a call. The certification audit is quoted and billed directly by the certification body.
An independent certification body, accredited to audit ISO 27001. It contracts with you and bills you directly. We are never the auditor and we take no share of its fee, because a fee split would compromise the independence that makes the certificate worth anything.
No control in Annex A of ISO/IEC 27001:2022 names penetration testing. The standard requires that technical vulnerabilities be identified and evaluated (A.8.8) and that security testing be part of development and acceptance (A.8.29). A penetration test is the most common way to evidence both.
If a buyer is asking for a SOC 2 report, yes: it is live today. Your agent, the MCP connection, the monthly pentest and your subscription stay the same when ISO 27001 opens.
Tell us your deadline and which framework your buyer asked for. We will tell you exactly what it takes.